Platform
Everything you needTo run production
A light control plane, an agent on every server, and everything else already wired.
Secure by design
No stored SSH keys. The agent calls out, the panel never calls in.
Versioned config
One shipkeep.yml per app, changed by commit or pull request.
Real multi-node
Placement and health checks. Target: failover in under 90 seconds.
Observability included
Planned: 30-day logs and metrics, with alerts.
Three steps to production
From an empty server to a live app, no Kubernetes and no root key.
Add a server
A 15-minute token. The agent enrolls and opens its outbound connection.
Push your code
Build, migrate, health check, switch. The old release serves until the end.
Observe
Logs, metrics and alerts for 30 days, nothing to assemble.
Secure by constructionNot by configuration
0
root keys
stored in the panel. The agent generates its own, on the host.
0
inbound ports for the agent
It calls out over mTLS. Only your sites’ traffic comes in, through Caddy.
< 90 s
failover target
when a server goes down. Databases will stay where they are.
Anatomy of a serverWhat runs on your machine
Five layers, from your Linux machine up to the agent, opening one by one.
Linux server
Your machine. Ubuntu, Debian or other, with systemd.
Docker Engine
Your apps and databases, each in its container.
Caddy
Automatic HTTPS and routing, driven over a Unix socket.
WireGuard
Private shipkeep0 network across all your servers.
shipkeep-agent
A Go binary. It calls the control plane, never the other way round.
Linux serveragent · ↑ mTLS :7443
One-click servicesAnd anything that fits in a container
Planned: managed databases with backups, and a catalog of Compose templates.
On any Linux server
HetznerOVHcloudScalewayDigitalOceanVultrRaspberry Pi
Open sourceIn the open
The control plane, the agent, the CLI and the threat model are public under Apache-2.0. Contributions are welcome.
Apache-2.0
Star on GitHub
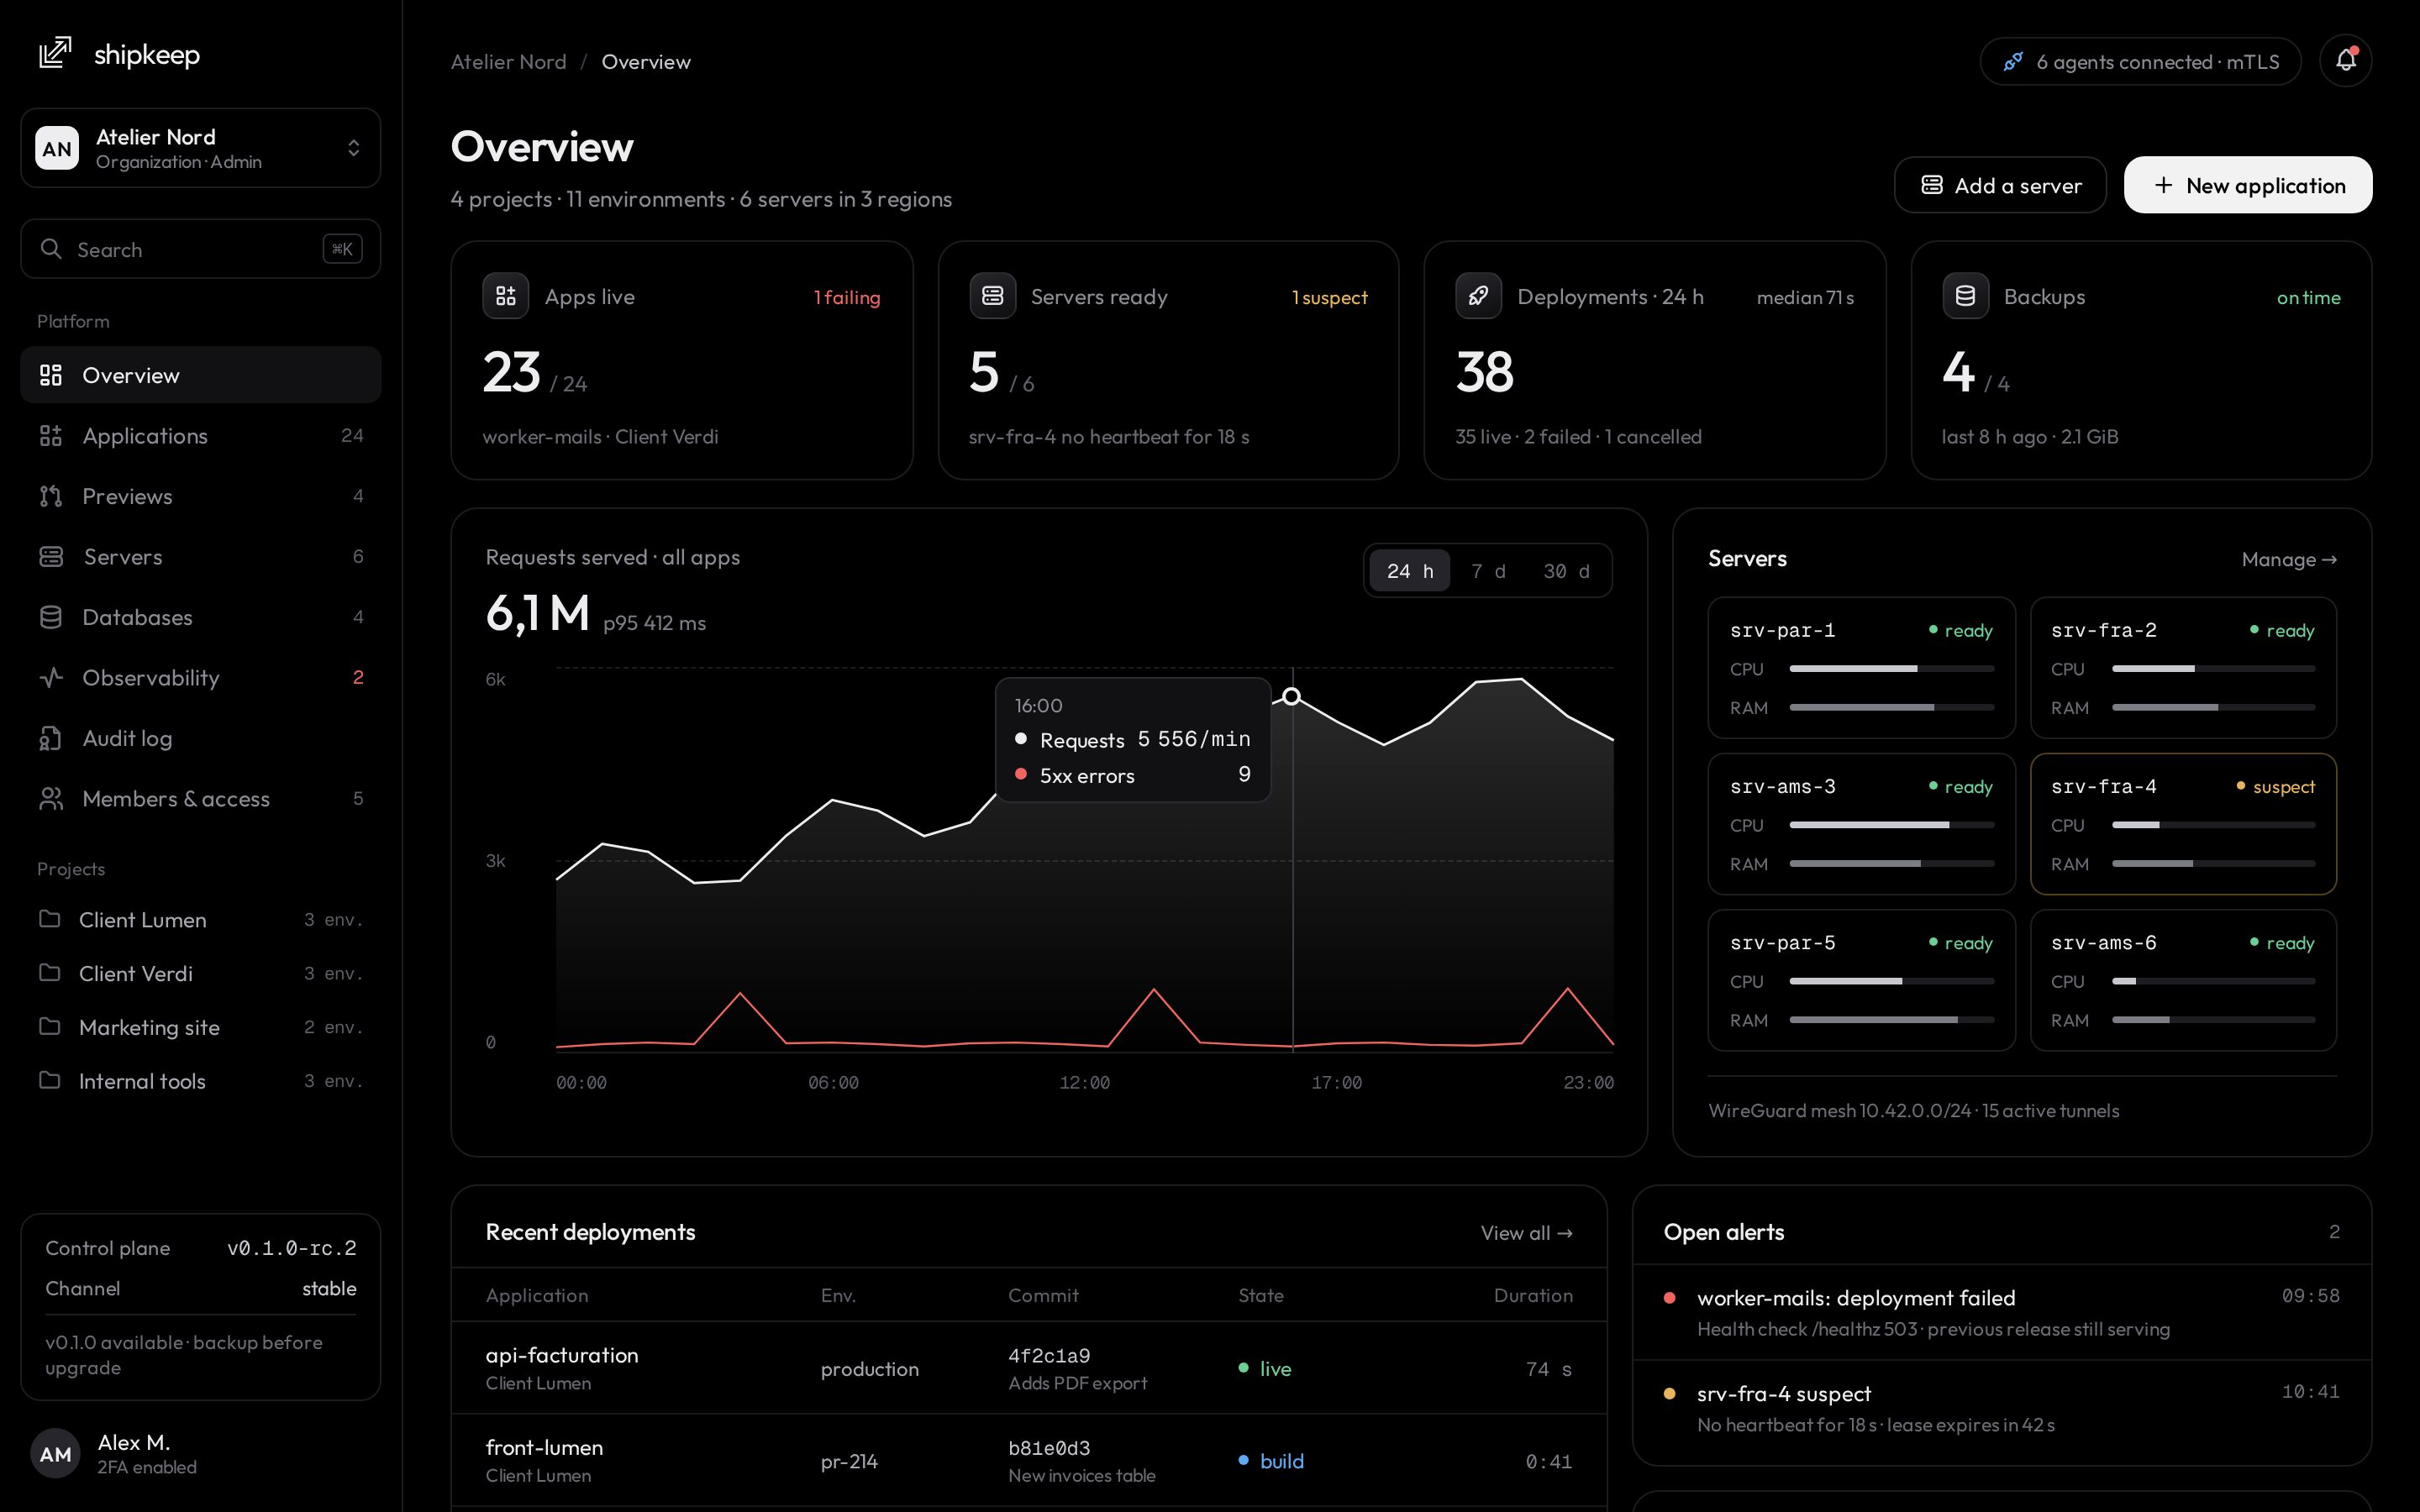
Requests served · example
18,6 M
26% vs last 7 days
Nov 1Nov 2Nov 3Nov 4Nov 5Nov 6Nov 7
What we promise
No panel will ever hold the root key to your servers.
docs/PRODUCT.md
CompareBefore you choose
ShipkeepCoolifyDokployKamal
Server connection
Outbound mTLS agentSSH root or sudoSSHSSH
Web interface
Config versioned in the repo
Compose onlyCompose only
Multi-node with failover
partialSwarmpartial
Users and roles
Managed databases
accessories
License
Apache-2.0Apache-2.0mixedMIT
Swipe to compare
Shipkeep column: what the first stable release aims for; the current prerelease covers part of it. Other columns: each project’s public documentation and license file, read on 11 November 2026.
Sources for Dokploy: connection · interface · config · settings · multi-node · roles · databases · license
FrequentlyAsked questions
Is Shipkeep really free?
Yes. Apache-2.0, no proprietary edition. A hosted version will come as an option.
Do I need Kubernetes?
No. Shipkeep places, monitors and fails over your Docker containers across servers.
What if the control plane goes down?
Your apps keep running. Each agent keeps its routing table and reconnects by itself.
Where do my secrets go?
Encrypted in PostgreSQL and sent only to the agent that needs them. The repo only holds their names.
Which servers are supported?
Any Linux server with systemd. The installer adds Docker, Caddy and WireGuard if needed.
Ready to take backThe keys to your cloud?
A prerelease can be installed to try it: installation guide. The code is public on GitHub.